(Reuters) – Speaking at a private dinner for tech security executives at the St. Regis Hotel in San Francisco in late February, America’s cyber defense chief boasted how well his organizations protect the country from spies.
U.S. teams were “understanding the adversary better than the adversary understands themselves,” said General Paul Nakasone, boss of the National Security Agency (NSA) and U.S. Cyber Command, according to a Reuters reporter present at the Feb. 26 dinner. His speech has not been previously reported.
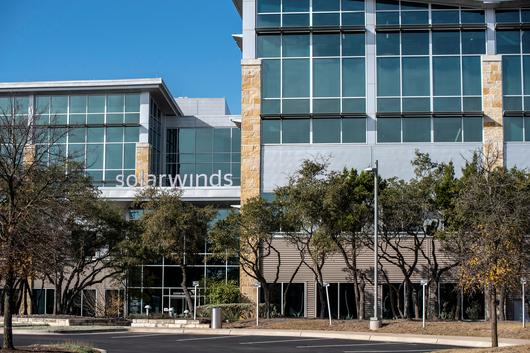
Yet even as he spoke, hackers were embedding malicious code into the network of a Texas software company called SolarWinds Corp, according to a timeline published by Microsoft and more than a dozen government and corporate cyber researchers.
A little over three weeks after that dinner, the hackers began a sweeping intelligence operation that has penetrated the heart of America’s government and numerous corporations and other institutions around the world.
The results of that operation came to light on Dec. 13, when Reuters reported that suspected Russian hackers had gained access to U.S. Treasury and Commerce Department emails. Since then, officials and researchers say they believe at least half-a-dozen U.S. government agencies have been infiltrated and thousands of companies infected with malware in what appears to be one of the biggest such hacks ever uncovered.
Secretary of State Mike Pompeo said on Friday Russia was behind the attack, calling it “a grave risk” to the United States. Russia has denied involvement.
Revelations of the attack come at a vulnerable time as the U.S. government grapples with a contentious presidential transition and a spiraling public health crisis. And it reflects a new level of sophistication and scale, hitting numerous federal agencies and threatening to inflict far more damage to public trust in America’s cybersecurity infrastructure than previous acts of digital espionage.
Much remains unknown — including the motive or ultimate target.
Seven government officials have told Reuters they are largely in the dark about what information might have been stolen or manipulated — or what it will take to undo the damage. The last known breach of U.S. federal systems by suspected Russian intelligence — when hackers gained access to the unclassified email systems at the White House, the State Department and the Joint Chiefs of Staff in 2014 and 2015 — took years to unwind.
U.S. President Donald Trump on Saturday downplayed the hack and Russia’s involvement, maintaining it was “under control” and that China could be responsible. He accused the “Fake News Media” of exaggerating its extent.
The NSC, however, acknowledged that a “significant cyber incident” had taken place. “There will be an appropriate response to those actors behind this conduct,” said NSC spokesman John Ullyot. He did not respond to a question on whether Trump had evidence of Chinese involvement in the attack.
Several government agencies, including the NSA and the Department of Homeland Security, have issued technical advisories on the situation. Nakasone and the NSA declined to comment for this story.
Lawmakers from both parties said they were struggling to get answers from the departments they oversee, including Treasury. One senate staffer said his boss knew more about the attack from the media than the government.